 Conduct a Security Assessment (Vulnerability Assessment) of Your Current Website
and Internal Network
Security Assessment
Attacks that exploit vulnerabilities in operating systems and applications are occurring with increasing frequency, and information leakage resulting from unauthorized access and targeted attacks continues to pose a serious threat.
Understanding the current state of systems to determine whether vulnerabilities exist, and implementing improvements based on the assessment results, is essential to strengthening overall security measures.
About Security Assessment
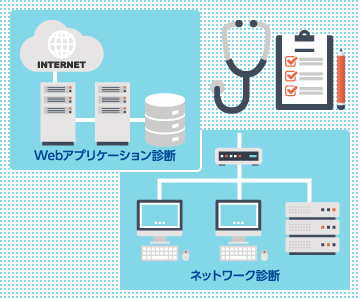
Security assessments conducted to identify the presence of vulnerabilities generally fall into two categories: "Platform Assessment" and "Web Application Assessment".
A Platform Assessment examines servers, network devices, operating systems, middleware, and related components to identify vulnerabilities and configuration flaws, while a Web Application Assessment examines web applications for vulnerabilities and configuration flaws.
Assessment methodologies include tool-based assessments and manual assessments performed by security consultants and engineers. Manual assessments can identify vulnerabilities and weaknesses that are difficult to detect using automated tools alone.
In addition, a "Penetration Test" evaluates the effectiveness of existing security measures by determining whether specific objectives can be achieved through simulated attacks. It is also referred to as an intrusion test. Penetration testing is also used as part of security assessment and investigation activities.
During a Penetration Test, realistic attack scenarios that would likely be used by actual attackers are developed, and simulated attacks are conducted. This approach investigates not only whether vulnerabilities exist, but also post-compromise behavior and the presence of information assets that could pose risks, providing an assessment from an attacker's perspective.
The Need for Security Assessments
Damage caused by attacks that exploit system vulnerabilities continues to occur, including personal information leakage, website defacement, system outages and access disruptions, and the use of compromised systems as attack platforms. When such incidents occur, they can result in substantial costs, including expenses for investigating the cause and implementing countermeasures, compensation for victims of information leakage, downtime costs, negative impacts caused by loss of trust from business partners, and, in some cases, fines for regulatory violations. To avoid these risks, it is necessary to provide opportunities to identify vulnerabilities that attackers could exploit.
Eliminating vulnerabilities and other security concerns also benefits the services you provide by allowing users to use them with confidence. In fact, in recent years, we have increasingly received inquiries from web application development companies whose customers require a third-party vulnerability assessment as a condition of delivery.
Differences Between Vulnerability Assessments and Penetration Tests
With growing awareness of security in recent years, we have received an increasing number of inquiries about these types of assessments. Because assessment providers sometimes use the terms "Penetration Test" and "Vulnerability Assessment" interchangeably, we often see cases where a Penetration Test is requested even though a Vulnerability Assessment would be more appropriate, or vice versa.
If you are considering an assessment to ensure that your systems are not exposed to attacks, please refer to the information below to determine whether a Penetration Test or Vulnerability Assessment is more appropriate.
| Vulnerability Assessment | Penetration Test | |
|---|---|---|
| Purpose | Comprehensively identify vulnerabilities and deficiencies in security functions | Verify whether an attacker with a specific objective could successfully achieve that objective |
| Scope | Each specified web application or IP address | Systems, people, organizations, and rules, covering either all systems owned by the organization or an entire specified system |
| Method | Examine system components against security standards and other criteria | Conduct simulated attacks to determine whether the objective can be achieved within a specified period |
| Report Contents | List of identified vulnerabilities and deficiencies in security functions | Results of attack scenario verification |
When to Conduct a Vulnerability Assessment
If any of the following applies to you, we recommend conducting a vulnerability assessment as soon as possible. Even if you use security products, some vulnerabilities cannot be protected against by those products.
- You have had a website publicly accessible on the Internet for some time but have never conducted a vulnerability assessment and would like to do so.
- You have not conducted a vulnerability assessment because you use security products, but have become concerned as you learned more about security.
If any of the following applies to you, we recommend conducting a vulnerability assessment before publication, allowing sufficient time for remediation after the assessment.
- You have created, expanded, or modified a website and want to identify vulnerabilities and risks before making it public.
- Your organization requires vulnerability assessments to be conducted periodically.
- The security requirements for a development project require a third-party vulnerability assessment before delivery.
- You have implemented secure programming based on guidelines and want to verify that it has been implemented correctly.
When creating, expanding, or modifying a website, we recommend conducting a vulnerability assessment before making it publicly accessible on the Internet. In addition, because new attack techniques are discovered every day, we also recommend conducting regular assessments of the entire website, approximately once a year.
For expansions and modifications, assessing only the areas that have changed and the areas affected by those changes can also significantly reduce risk.
In fact, we sometimes receive inquiries such as,
"We did not conduct a vulnerability assessment because our website does not contain personal information, but a business partner required one as part of its supply chain security measures," or
"We conducted an assessment once before launching the service, but several years have passed since then, and a customer raised concerns."
When an assessment is conducted, multiple high-risk vulnerabilities are sometimes identified. Ideally, an assessment should be conducted once before publication and then regularly once a year thereafter.
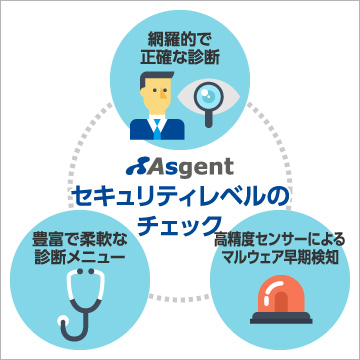
Security Level Assessment by Asgent: Three Key Features
-
Vulnerability Assessment by Experienced Security Engineers
Our experienced security engineers assess systems from an attacker’s perspective, reflecting business requirements and system specifications, and addressing the latest attack techniques based on up-to-date threat intelligence. -
Tailored Assessment Methods Optimized for Each Customer
Asgent offers a wide range of vulnerability assessment services, from automated tool-based testing to in-depth manual assessments. Asgent’s engineer proposes the most appropriate assessment approach based on each customer’s budget and security requirements.
For both automated and manual assessments, experienced security engineers conduct a formal results briefing based on the assessment report and provide clear recommendations for remediation and next steps, ensuring confidence and transparency throughout the process. -
Security Solution Recommendations After Vulnerability Assessment
While many assessment services provide remediation guidance in their reports, identifying and selecting appropriate security solutions can be time consuming. Asgent offers a broad portfolio of security products and services and can recommend optimal security solutions to effectively mitigate the vulnerabilities identified during the assessment.
Services and products
- Asgent’s security assessment (vulnerability assessment) services include free initial consultation and quotation. Please feel free to contact us.
 Connected Car
 File Sanitization
 Targeted Attack Protection
 Web Security
 Email Security
 Mobile
 Cloud
 Security Assessment
 Risk Management
 For Local Governments
 Supply Chain
 Zero Trust
