 Japan’s No.1 Email and File Sanitization Solution*1 (FY2023, by revenue)
(Source: ITR “ITR Market View: Endpoint / Secure Browser / Micro-Segmentation / Content Disarm & Reconstruction / CNAPP / DSPM / XDR Market 2025”)
*1 Votiro Disarmer and Votiro Secure File Gateway
Votiro Disarmer
(Source: ITR “ITR Market View: Endpoint / Secure Browser / Micro-Segmentation / Content Disarm & Reconstruction / CNAPP / DSPM / XDR Market 2025”)
*1 Votiro Disarmer and Votiro Secure File Gateway
It has been deployed by more than 750 local governments across 46 prefectures, as well as by financial institutions, healthcare organizations, life and non-life insurance companies, broadcasters, and many other private-sector organizations (as of January 2019).
In recent years, targeted attacks have increased, exposing many organizations to greater risk. Traditionally, many targeted attacks have attempted to infect endpoints with malware and steal confidential information by disguising malicious emails as legitimate messages. More recently, however, infection vectors have diversified, with malware increasingly being introduced not only through email but also through files downloaded from websites and files brought into organizations on privately owned USB drives.
Because malware source code can be easily obtained from the Internet and customized, numerous new malware variants continue to emerge. As a result, conventional security measures that rely on pattern matching, such as antivirus products, are reaching their limits, making effective malware protection an urgent priority for organizations.
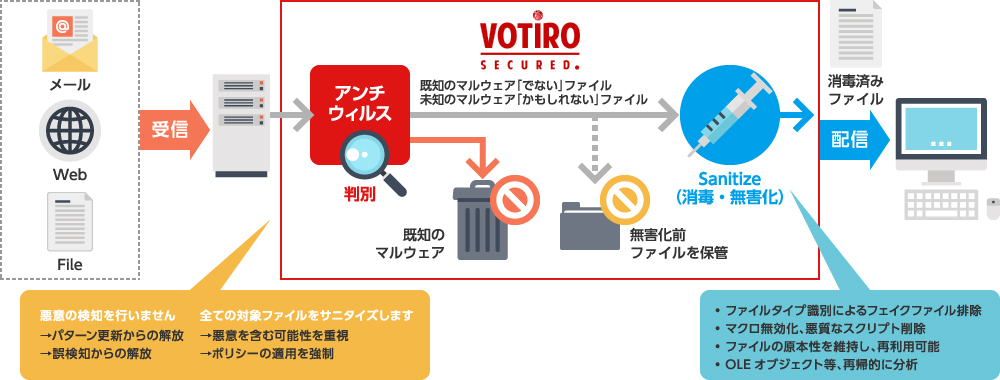
Votiro Disarmer focuses on the possibility that a file may contain malware and sanitizes all applicable files entering an organization from external sources through various channels, including email and the web.
Key Features
-
Sanitizes All Target Files to Block Targeted Attacks
Unlike conventional products relying on pattern matching or signature-based detection, Votiro Disarmer inspects these critical data areas. It sanitizes attack executables by either eliminating data sections unnecessary for file operation or by injecting nonsensical data. By sanitizing all targeted files, regardless of whether malice is detected, the solution defends against unknown zero-day threats for which no signatures exist. This simultaneously frees organizations from the burden of continuous pattern updates and the hassle of false positives. Specifically, Votiro Disarmer prevents sophisticated targeted attacks and subsequent data leakage by completely sanitizing malware embedded in files imported from external sources.
-
Broad Support for File Formats
Votiro Disarmer supports virtually all commonly utilized file formats, including Microsoft Office files, PDF documents, image files, and many others.
Microsoft Office & Related Files Excel, Word, PowerPoint, RTF, Visio 2013 and later
Identifies and sanitizes internal components such as macros and embedded objects within documentsIchitaro files JTD,JTDC (JustSystem document formats)
Removes macros, sanitizes images and OLE objects, and reconstructs safe filesPDF files Maintains essential functions like text copy search capabilities even after sanitization Image files BMP,GIF,WMF,EMF,PNG,JPG,JPEG,TIFF,TIF,WDP
Conducts file analysis at the pixel levelCompressed files ZIP,Microsoft-CAB,TAR,RAR,7Z,GZIP,GZ
Supports nested (multi-layer) compressed files
Allows for recompression after sanitization
Supports password-protected archivesDocuWorks 8/9 XDW
Limited to file-type recognition and anti-virus scanning onlyAutoCAD DWG,DXF
Removes macros, OLE objects, and images; reconstructs safe filesJWW CAD JWW
Sanitizes embedded images and reconstructs safe filesSXF CAD SFC,P21
Sanitizes files and reconstructs safe versions*For file types not listed above, please contact us for more information.
Product Lineup
| Disarmer File Connector | Disarmer Web Service |
|---|---|

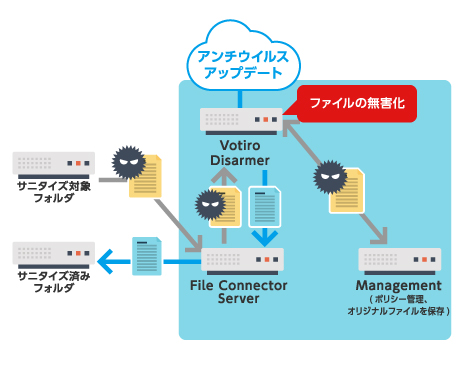
Integration with File Servers and FTP Servers for Sanitization |
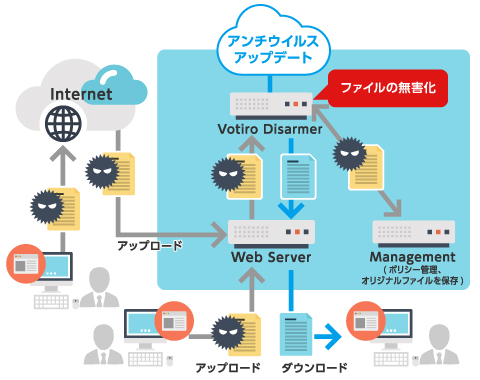
Integration with Web Servers for Sanitization |
 |
 |
| Disarmer Email Connector | Disarmer Web Adapter |
|
Integration with All SMTP Mail Servers for Sanitization |
Provides Approval Control for File Transfers Between Network Segments |
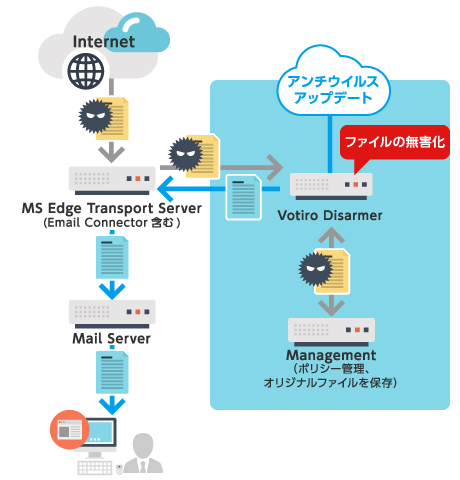 |
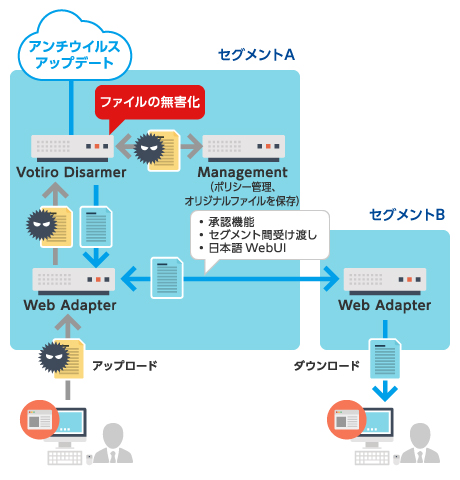 |
Deployment Patterns
Deployment Pattern 1: As a Method of "Sanitized Communication" for Local Governments
In the report "Toward Fundamental Enhancement of New Information Security Measures for Local Governments," released by the Ministry of Internal Affairs and Communications and published by the Local Government Information Security Measures Study Team in November 2015, it is recommended that communication paths be separated between business systems using LGWAN, such as financial accounting systems, and systems used for web browsing and Internet email, in order to ensure the security of the WAN environment used for information coordination involving My Number. The report also recommends that when communication is required between the two systems, sanitized communication that prevents virus infection should be implemented. Votiro Disarmer is proposed as a means of achieving this "sanitized communication."
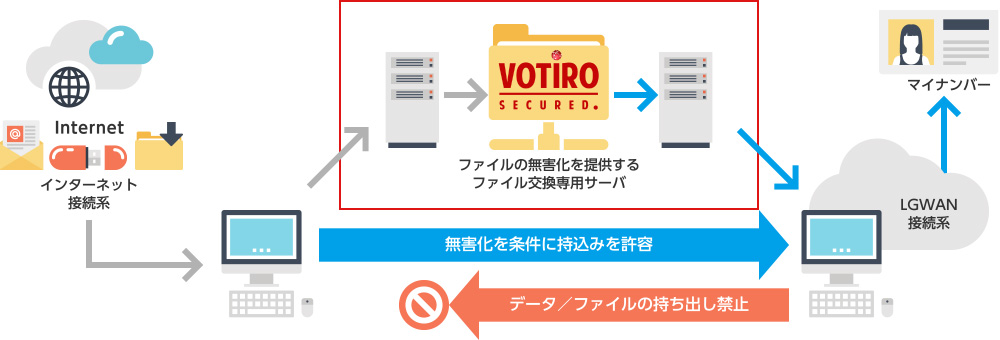
Assumed Policy
| Category | Internet-Connected LAN | LAN for Personal Number-Related Administrative Work, etc. | LAN for Personal Number Administrative Work |
|---|---|---|---|
| Web Access | Via integrated proxy | Prohibited | Prohibited |
| External Email (Incoming) | Via integrated email platform (Antivirus / Sandbox) |
From Internet-connected terminal Via sanitization engine |
Prohibited |
| External Email (Outgoing) | Encryption / Misdirected Email Prevention / Audit Trail | Prohibited | Prohibited |
| Bringing in Physical Media | Via sanitization engine | Prohibited | Prohibited |
Deployment Pattern 2: File Sanitization Measures for Financial Institutions
Many financial institutions have a high level of security awareness regarding threats such as ransomware and other malware infections. However, even among financial institutions that have actually experienced security incidents, relatively few have increased their security budgets. Nevertheless, threats arising from this gap between ideal security and actual conditions can become a reality, making it necessary to implement advanced file sanitization measures. Votiro Disarmer provides such protection.
Financial institutions need to prevent malware infections not only in information systems connected to the Internet, but also in core banking networks that handle customer information and financial transactions.
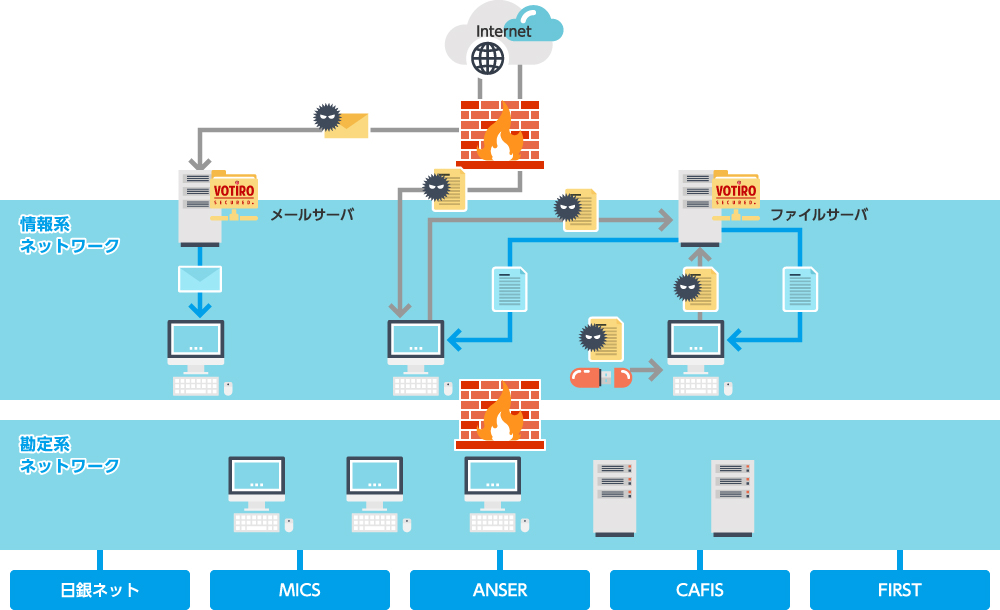
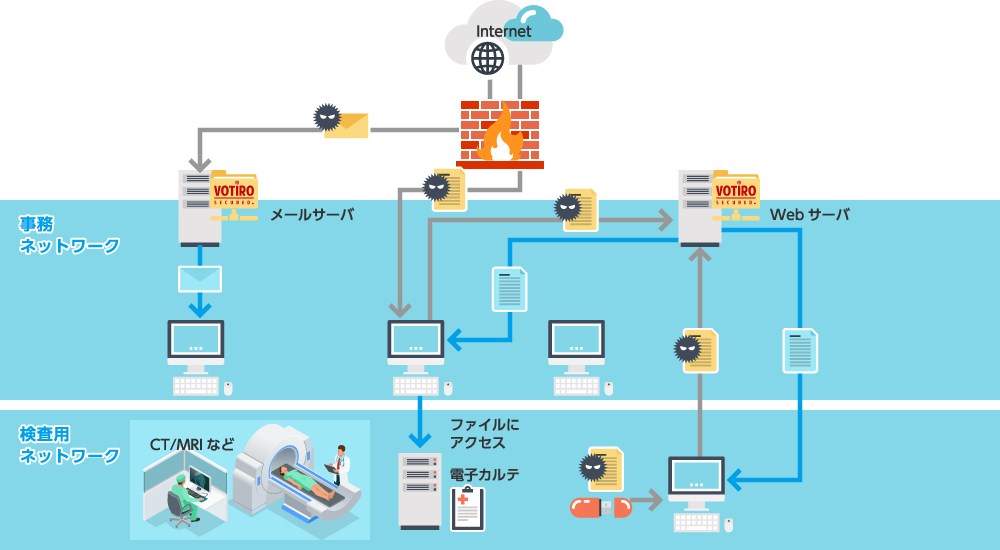
Deployment Pattern 3: File Sanitization for Healthcare Environments Handling Large Amounts of Personal Information
The "Guidelines for the Safety Management of Medical Information Systems," issued by the Ministry of Health, Labour and Welfare in 2017, call for the implementation of specific security measures in the healthcare sector. In healthcare environments such as hospitals and clinics, where large amounts of personal information are handled, information leakage resulting from malware infection cannot be tolerated. However, cases of hospitals and national health services overseas being infected with ransomware and other malware have actually occurred. This is therefore no longer a problem that can be regarded as "someone else's concern," and organizations should consider implementing Votiro Disarmer.
Security Products
- Next-Generation Firewall
- Targeted Attack Protection
- Cloud Security / Virtualization
- Mobile / Endpoint Security
- Email Security
- Anti-Phishing
(BEC etc.) - Application Security
- Server Security
- Sandbox
- File Sanitization
- Log Analysis
- Server Monitoring
- Encryption
- Security Policy
- Industrial Control System Security
- Connected Car Security
- WAAP
- Browser Security
- Cloud Backup
- SASE
- ASM
- Vulnerability Management
- Security for AI
