 A Support Tool for Efficiently Building and Operating ISMS and PMS
M@gicPolicyCoSMO
Compliant with JIS Q 27001:2023 (ISO/IEC 27001:2022)
In recent years, companies have been increasingly required to fulfill their accountability from various perspectives, including compliance with laws and regulations such as the Act on the Protection of Personal Information, the Unfair Competition Prevention Act, and J-SOX, as well as business continuity management (BCM), improved customer service, and ensuring safety.
Under these circumstances, building and operating an Information Security Management System (ISMS) and a Personal Information Protection Management System (PMS) have become more important than ever as the infrastructure needed to meet these requirements. However, building an effective ISMS or PMS requires considerable expertise and time, placing a heavy burden on security personnel. Organizations may also face various challenges in continuing to operate an ISMS or PMS after it has been established. M@gicPolicyCoSMO (Corporate Security Management Operator) is a tool designed to address these challenges and efficiently support the establishment, operation, and maintenance of ISMS and PMS.
M@gicPolicyCoSMO was developed under the design supervision of Akihiko Komase, Fellow at the Asgent Security Center.
Key Features of M@gicPolicyCoSMO
-
Centralized Server-Based Data Management Enables Real-Time Operations
M@gicPolicyCoSMO is an application installed on a server within the organization. Users can access M@gicPolicyCoSMO over the intranet and perform various tasks simultaneously. The results of these tasks are reflected in the M@gicPolicyCoSMO database in real time, significantly reducing the administrative workload required to aggregate, evaluate, revise, and otherwise manage data updated by each department.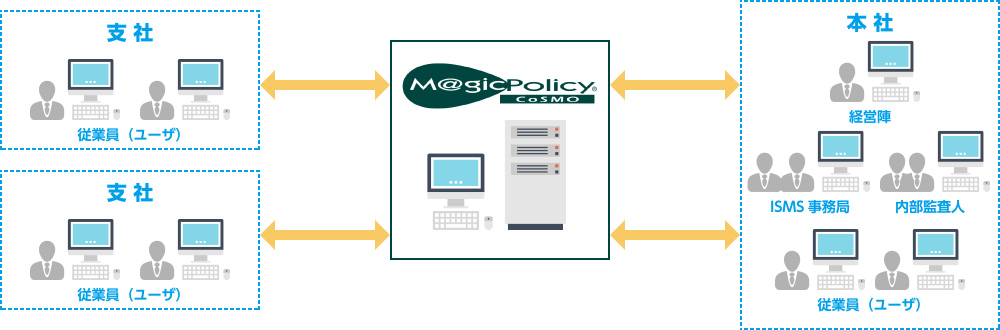
-
Supports Every Stage of the PDCA Cycle Essential for Building and Operating ISMS and PMS
M@gicPolicyCoSMO provides functions for carrying out ISMS and PMS activities in accordance with the PDCA cycle. By following the menus, users can perform activities that correspond to the requirements of applicable standards.
By managing various ISMS and PMS activities with M@gicPolicyCoSMO, organizational activities are consolidated in a centralized database. This eliminates the need to rush to collect data and results when preparing for audits and other reviews.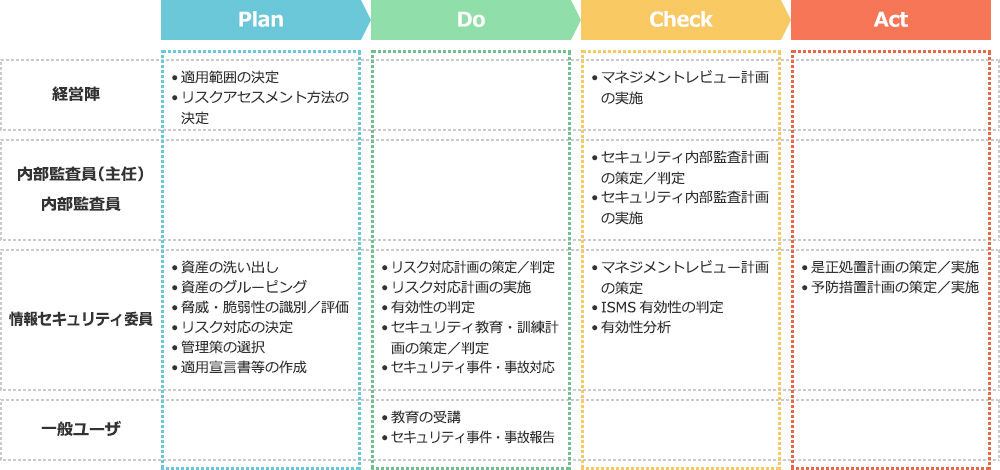
-
Standardized and Efficient Risk Assessment
For risk assessment in the ISMS version, a list of asset-related threat and vulnerability tables is provided, allowing users to identify and evaluate risks using the risk information provided by the tool. The system also automatically selects appropriate recommended controls based on the identified threats and vulnerabilities, enabling effective and comprehensive selection of security controls. For the PMS version, risk identification templates are provided for each stage of the personal information handling lifecycle, from acquisition through disposal and deletion. These templates support efficient risk identification and analysis. The system also includes functions for planning and managing measures to address residual risks.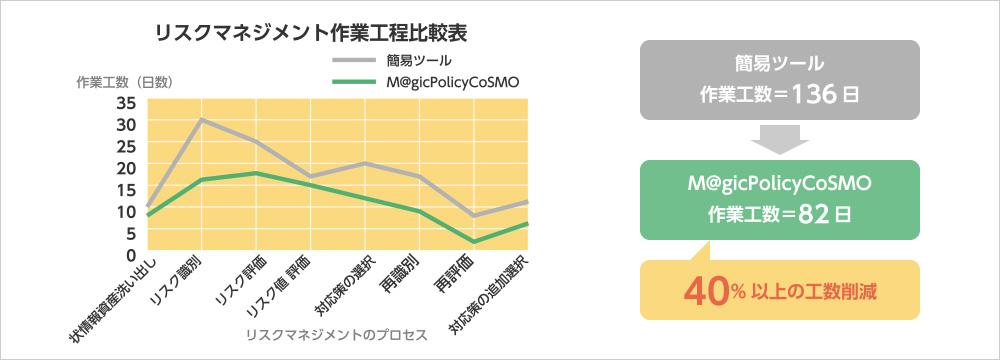
-
Security Education and Training for Proactive Improvement of ISMS and PMS
Based on the training schedule created by the person responsible for education, M@gicPolicyCoSMO automatically distributes To Do lists and emails prompting participants to take training courses and tests. The person responsible for education can use the participants’ responses to understand, in real time, their level of awareness regarding information security and personal information protection. Tests can also be conducted periodically, and participants who do not pass can be required to retake them. -
Internal Audits
In the ISMS version, M@gicPolicyCoSMO automatically identifies the implemented controls and can present audit items related to those controls. These audit items are based on ISO/IEC 27002 and JIS Q 27002. Internal auditors can use the presented audit items as well as their own organization-specific audit items, while dividing audit work among multiple internal auditors. Based on an internal audit plan created by the lead internal auditor, the system can also distribute each auditor’s assigned audit tasks as a To Do list and support the execution of internal audits. The PMS version includes standard internal audit items based on JIS Q 15001 and the second edition of the “Guidelines for Implementing a Personal Information Protection Management System Based on JIS Q 15001:2006” issued by JIPDEC. By selecting items appropriate to the audit objectives, organizations can carry out internal audits and inspections. As with the ISMS version, users can also combine the presented audit items with organization-specific audit items and divide the internal audit work among multiple auditors.
Deployment Patterns
Deployment Pattern 1: [Non-Life Insurance] Sony Assurance Inc.
- ■Challenges
-
Insufficient manpower in the administrative office
Reducing the workload on operational departments involved in promoting ISMS activities
Standardizing and streamlining risk assessment for a vast amount of information assets - ■Benefits
- By implementing M@gicPolicyCoSMO, we were able to carry out the tasks required to establish an ISMS simultaneously and efficiently throughout the company.
Background to Focusing on the Information Security Management System (ISMS)
As a direct insurance company, we hold a large volume of customer information.
Since our company was still relatively young, we believed that earning the trust of our customers was essential for the company to survive and grow. Even if our business performance were strong, an information leakage incident or similar event could result in the loss of public confidence and trust, potentially threatening the continuity of our business and even the survival of the company.
Because our business model is based on direct insurance, we communicate directly with customers by telephone and over the Internet. Security in these communications is therefore critical to business continuity. To earn the trust of our customers, we identified strengthening information security and thoroughly implementing ISMS activities as key priorities.
To promote information security, we had already implemented various measures within our internal infrastructure, including an access control system using ID card authentication and surveillance cameras. However, rather than implementing individual measures in isolation, we decided to establish an Information Security Management System and pursue certification as one of our objectives so that we could create a more effective management cycle and embed information security throughout the organization.
In 2005, we were among the first in the industry to obtain certification under BS7799, covering our head office-related departments (planning and administration departments) and system departments.
However, our efforts did not stop with this initial scope. As mentioned above, our most important information assets are customer information, much of which is handled by operational departments such as the Customer Center (call center), which accepts contracts, and the Service Center, which responds when accidents occur. We therefore continued our efforts to expand the scope to the entire company. As a result, in 2007 we became the first company in the industry to obtain ISO/IEC 27001 certification covering the entire organization.
These activities not only demonstrated our commitment to protecting valuable customer information and providing customers with confidence when purchasing insurance, but also contributed significantly to raising security awareness among individual employees.
Challenges in Establishing an ISMS
The greatest challenge in promoting our ISMS was the limited manpower available because our company was still in a growth stage. The administrative office had no dedicated personnel and was operated by three employees who were also responsible for their primary duties. At the same time, it was essential to establish efficient operations that minimized the burden on operational departments and did not interfere with their core responsibilities.
In addition, because we have offices in major cities throughout Japan, it was difficult to share expertise such as risk assessment methods consistently across all locations. We also had many temporary employees and staff from partner companies, which made it challenging to maintain consistent information security controls.
Benefits and Advantages of Implementing M@gicPolicyCoSMO
To thoroughly promote our ISMS and strengthen the administrative office, we introduced M@gicPolicyCoSMO together with hands-on consulting support.
The implementation of M@gicPolicyCoSMO eliminated much of the complexity involved in risk assessment and enabled us to manage information assets and conduct risk assessments in a standardized manner across all of our locations nationwide. One particularly valuable benefit was the ability to easily assign risk levels to information assets via the web and manage them in a centralized list.
We also appointed an "ISMS Committee Member" in each department to conduct departmental risk assessments. Because M@gicPolicyCoSMO provides a workflow based on certification requirements, even committee members who were not deeply familiar with ISMS could perform the required tasks easily.
In addition, the consulting support enabled us to thoroughly identify security vulnerabilities and other issues within the company. The accurate advice we received clarified the challenges we needed to address and enabled us to develop more effective risk treatment plans.
Even with limited administrative resources, we were able to carry out the tasks required to establish the ISMS simultaneously and efficiently throughout the company and smoothly obtain ISO certification company-wide. We believe it is no exaggeration to say that this was made possible through the introduction of M@gicPolicyCoSMO and consulting support.
Deployment Pattern 2: [Telecommunications Carrier] NTTPC Communications, Inc.
- ■Challenges
-
The enormous amount of effort required for risk assessments and other measures was interfering with the annual ISMS activity plan.
Each time the risk analysis methodology was changed, the risk assessment process had to be restarted from the beginning.
Assigning tasks according to the division of responsibilities increased the amount of work required. - ■Benefits
- By implementing M@gicPolicyCoSMO, the workload required for risk assessments was significantly reduced, enabling us to maintain ISMS activities as intended.
Background to Focusing on the Information Security Management System (ISMS)
At NTTPC Communications, we regard security as one of the most important aspects of our business activities and have actively pursued the highest levels of security. Our services cover a wide range of areas, including network services that build optimal network environments based on large-scale infrastructure and highly reliable operational structures; on-demand services that quickly provide the best solutions by combining services, technologies, and products; centralized corporate billing services that improve the efficiency of customers' accounting operations; and related network construction, maintenance, and system development. We have always made every effort to ensure a high level of information security across all of our solutions. To further demonstrate this commitment to our stakeholders as part of our Corporate Social Responsibility (CSR), we obtained ISMS certification in February 2005.*1 Initially, the certification covered only part of the organization, but during the 2007 surveillance audit, the scope was expanded to the entire company. Since then, we have continued our efforts to progressively improve information security based on CSR. *1 Certification Registration No. IS 89520 / JIS Q 27001:2006 (ISO/IEC 27001:2005)
Challenges in Establishing an ISMS
Three years after obtaining ISMS certification in 2005, we came to recognize that continuously maintaining the PDCA management cycle was even more important than obtaining the certification itself. However, in maintaining and continuing these activities, the enormous amount of work required for periodic risk assessments became one of the major challenges in operating the PDCA management cycle. Risk assessments require specialized knowledge as well as significant effort. In terms of knowledge, whenever the risk analysis methodology was changed, explanations had to be provided again and the process effectively had to start over from the beginning. In terms of workload, risk assessments were conducted separately by each department using paper documents and spreadsheet software, which required considerable time and effort. In addition, the complexity of our division of responsibilities made coordination among departments another source of difficulty. Although risk assessment is of course important, clearly defining and managing numerous other ISMS activities, such as internal audits and education and training, is also essential to ensuring that the ISMS functions effectively. We therefore strongly believed that reducing the operational burden would enable us to carry out more effective and reliable ISMS activities as intended.
Benefits and Advantages of Implementing M@gicPolicyCoSMO
・Effective and efficient risk assessments
・Progress management for plans and corrective measures
Following the 2007 surveillance audit, we began considering the introduction of tools for establishing and operating our ISMS. Many ISMS-related tools generally focus on document management, but M@gicPolicyCoSMO provides comprehensive support for risk assessments and various other ISMS activities based on the PDCA cycle. We therefore determined that it would enable us to continue managing the ISMS we had established in a comprehensive manner and decided to implement it.
M@gicPolicyCoSMO enables ISMS operations to be carried out through the company's internal portal site. For risk assessments, centralizing information assets on the web enabled us to identify information assets more efficiently. In particular, we were able to reduce the workload required for highly time-consuming tasks such as identifying information assets, evaluating and grouping asset values, and identifying and evaluating threats and vulnerabilities. Because the system includes the processes and methodologies required to conduct risk assessments that comply with ISO/IEC 27001 requirements, we believe we were able to conduct standardized risk assessments appropriately. We also believe that variations were minimized, helping to ensure the reproducibility of risk assessments required by the standard. Because risk assessment results could be reviewed using various reports throughout the process, we were able to quickly determine risk acceptance criteria and levels, select effective controls based on risk assessment results, and develop efficient risk treatment plans.
With regard to coordination between departments and progress management for various plans, when tasks are assigned to individual departments, it is important to continuously monitor the progress of each department and provide support to departments experiencing delays. M@gicPolicyCoSMO provides functions that support the various ISMS plans developed as part of ISMS activities within an intranet environment. By making full use of these functions, we were able to centrally manage plan schedules with clearly assigned responsibilities. We could also easily manage tasks assigned to individual departments and identify departments experiencing delays, which made operations smoother. Activity records can also be centrally managed. Previously, when information was requested internally or externally, considerable time was required to compile and edit materials. We can now use the data stored in M@gicPolicyCoSMO directly for presentation or process it as necessary, reducing the amount of work required.
In conclusion, at NTTPC Communications we highly value the fact that implementing M@gicPolicyCoSMO has enabled us to maximize its benefits, improve the efficiency of our ISMS activities, and focus more closely on the fundamental purpose of ISMS activities—that is, continuously improving the PDCA management cycle.
«Items used internally by the company to promote ISMS activities»
・"Laptop Management" stickers
・"Clear Desk / Clear Screen" stickers
・"Security Patrol" armbands
Security Products
- Next-Generation Firewall
- Targeted Attack Protection
- Cloud Security / Virtualization
- Mobile / Endpoint Security
- Email Security
- Anti-Phishing
(BEC etc.) - Application Security
- Server Security
- Sandbox
- File Sanitization
- Log Analysis
- Server Monitoring
- Encryption
- Security Policy
- Industrial Control System Security
- Connected Car Security
- WAAP
- Browser Security
- Cloud Backup
- SASE
- ASM
- Vulnerability Management
- Security for AI
